Table of Contents
How Remote PPC Teams Can Share Files More Securely
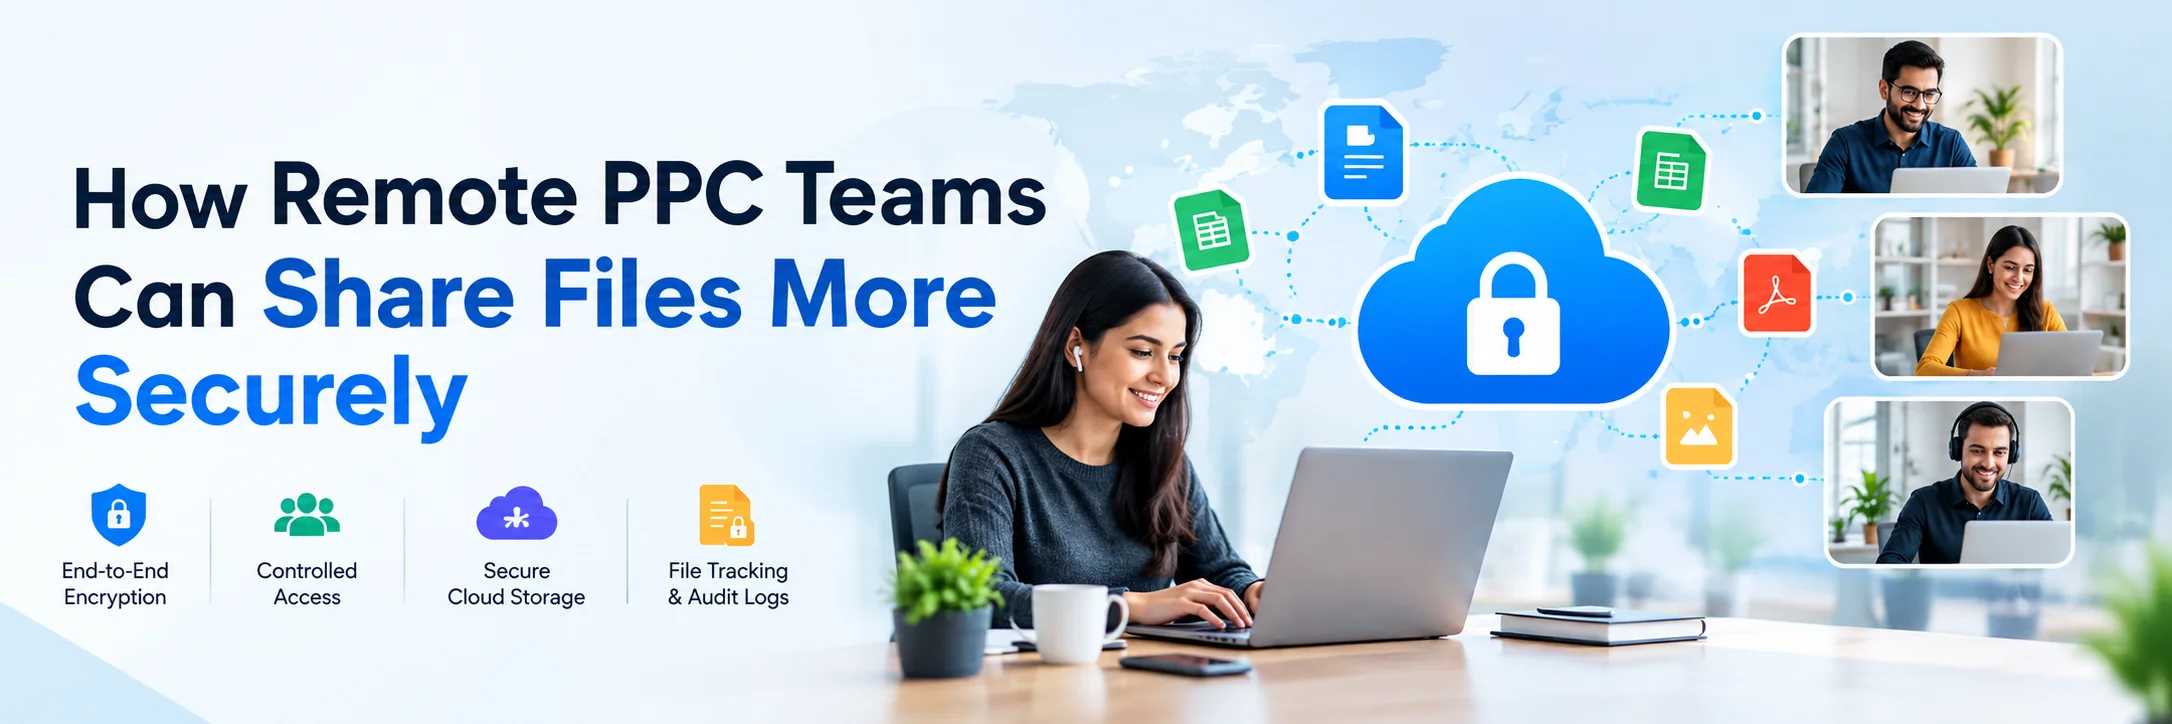
If you run a PPC agency with freelancers and contractors scattered across different cities or countries, you already know the upside of remote work. Smaller overheads, a wider talent pool, and people who can jump into campaign builds at short notice. But that flexibility creates a problem most agency owners don't think about until something goes wrong: where are your client files actually sitting, and who still has access to them?
Campaign data isn't trivial. We're talking about conversion tracking setups, audience lists, ad creative tied to unreleased products, and login credentials for client ad accounts. When that kind of information lives on a freelancer's personal Google Drive or gets pinged across WhatsApp, the exposure is real and can be devastating. So let's get into the specific risks and the controls that will actually make a difference.
Personal Cloud Accounts Are the Weak Link
Most freelancers default to whatever cloud tool they already use. That's usually a free personal account with no admin oversight, no audit trail, and no expiry on shared links. A media buyer downloads a client's customer match list to their personal Dropbox, does the work, and moves on to the next project. That file doesn't disappear. It sits there, accessible, possibly synced to a phone, indefinitely.
The Cyber Security Breaches Survey revealed that 43% of UK businesses reported a cyber attack in the previous 12 months. For small agencies without dedicated IT teams, the risk is often higher because there's no one watching the gaps between projects.
The fix doesn’t necessarily have to be highly sophisticated, but it does need to be deliberate. Set a policy that all client work stays on company-approved platforms. If a freelancer needs to access a file, they get a shared link with an expiry date, not a permanent download.
Least-Privilege Access Saves You From Mistakes
One of the most common errors in remote PPC setups is giving every team member access to everything. A new contractor joins to run Shopping campaigns, and suddenly they can see every client's Google Ads account, every shared drive folder, and every reporting dashboard.
Least-privilege access means people only see what they need for the specific job they're doing. If a freelancer is working on one client's Meta campaigns, they don't need access to another client's conversion data or keyword research files. This limits the damage if an account is compromised, and it limits the mess if someone simply makes a mistake.
Most cloud platforms let you set folder-level permissions. Use them. And keep a simple spreadsheet that tracks who has access to what, updated every time someone joins or leaves a project.
The Right File-Sharing Setup for a Distributed Team
Not all cloud platforms treat your files the same way. Most of the big providers encrypt files in transit and at rest, but they also hold the encryption keys themselves. That means the provider can technically access your data, and so can anyone who compromises the provider.
For agencies handling sensitive client data, end-to-end encrypted cloud storage closes that gap. Many popular storage providers encrypt files on the device before they're uploaded, and they never hold a readable copy. It’s a bonus if they also offer password-protected sharing links with expiry dates, which will solve the "lingering access" problem that plagues most agency workflows.
Pay attention to where the servers are as well. The data jurisdiction question has to have a clear answer, which matters when your team members span multiple countries. If a freelancer in one country stores a UK client's conversion data on a server in another jurisdiction, you could be creating a compliance issue without realising it. GDPR doesn't stop at borders, and the ICO has made it clear that data controllers are responsible for knowing where personal data is processed.
Offboarding Is the Step Most Agencies Skip
When a freelancer finishes a project, the typical process is: pay the invoice, say thanks, and move on. What most agencies don't do is revoke access.
That freelancer might still have a live link to the client's shared folder. They might still be logged into a reporting tool. Their browser might still have saved passwords from your ad accounts. It doesn’t mean it’s malicious, but it's all exposure. Build a simple offboarding checklist with these few steps as a baseline:
- Revoke all shared file links tied to that person
- Remove them from any project management or reporting tools
- Change passwords on any shared accounts they had access to
- Check cloud platform logs for any files downloaded in the final week
This should take no more than half an hour. But skipping it could cost you a client relationship or worse.
Why Data Jurisdiction Matters More Than You Think
When your team is spread across the UK, Europe, and beyond, the physical location of your file storage has legal weight. Different countries have different rules about government access to stored data, and some jurisdictions offer weaker protections than others.
If your agency stores client data on US-based servers, that data may be subject to US law enforcement requests under CLOUD Act provisions, even if your agency and your client are both based in the UK. That's a conversation most PPC agencies haven't had, but it's one worth having, especially if your clients operate in regulated sectors like finance, healthcare, or legal services.
Choosing a storage provider based in a strong privacy jurisdiction, like Switzerland, gives you a cleaner answer when clients ask where their data lives. It's a small detail that builds trust.
What Secure File Sharing Actually Looks Like Day to Day
None of this has to be painful. The goal isn't to slow your team down with red tape. It's to build a few simple habits that protect your agency and your clients without adding friction to the work.
Start with three things: a company-approved cloud platform with proper encryption, a clear access policy that follows least-privilege rules, and an offboarding checklist that gets used every single time. Get those right, and you'll have closed the biggest gaps most remote PPC teams don't even realise are there.
Final Thought
Secure file sharing is not about making remote PPC work complicated; it is about creating a system where sensitive client data remains protected at every stage of a campaign. Using company-approved storage, end-to-end encryption, least-privilege access, secure sharing links, and a consistent offboarding process can significantly reduce unnecessary exposure.
Remote teams can still work quickly and flexibly, but security needs to be built into their everyday workflow. When agencies know where client data is stored, who can access it, and when that access should end, they can protect valuable information while building greater trust with clients.
 +91 774-202-1725
 +1 (945) 3387904
 business@coherentlab.com
 +49 15223341304
 UK